1
Arm
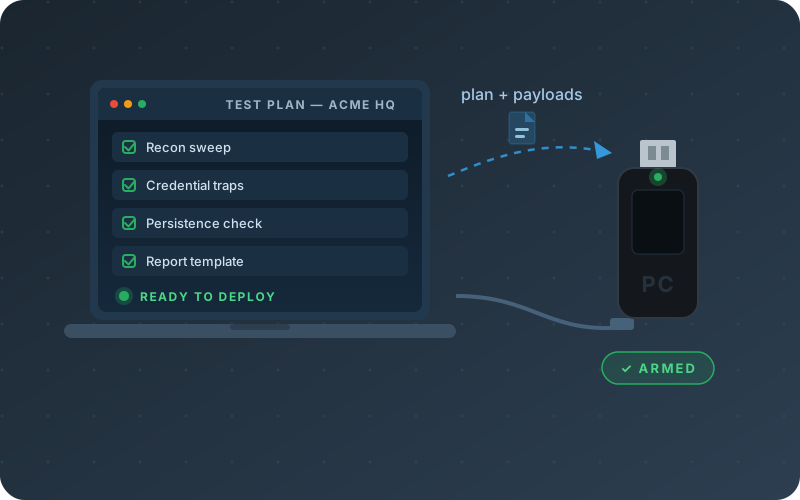
Expert · before travelA security expert loads the test plan onto the device before anyone travels. Devices are armed per engagement and reused.
Advanced hardware solutions for authorized security assessments and red team operations
Our specialized penetration testing devices provide security professionals with powerful tools for comprehensive security assessments. These devices enable real-world attack simulations, network monitoring, credential harvesting, and infrastructure testing in controlled, authorized environments.
Each device is designed for professional use in authorized penetration testing engagements, security audits, and red team exercises. They combine cutting-edge technology with practical functionality to help identify vulnerabilities before malicious actors can exploit them.
The device holds the method, so the person on site does not need to be the expert. Results are identical no matter who plugged it in, and one specialist can run several engagements in parallel.
A security expert loads the test plan onto the device before anyone travels. Devices are armed per engagement and reused.
Any available person connects the device: a field technician, a junior, whoever is free. No laptop, no tools; a phone is enough.
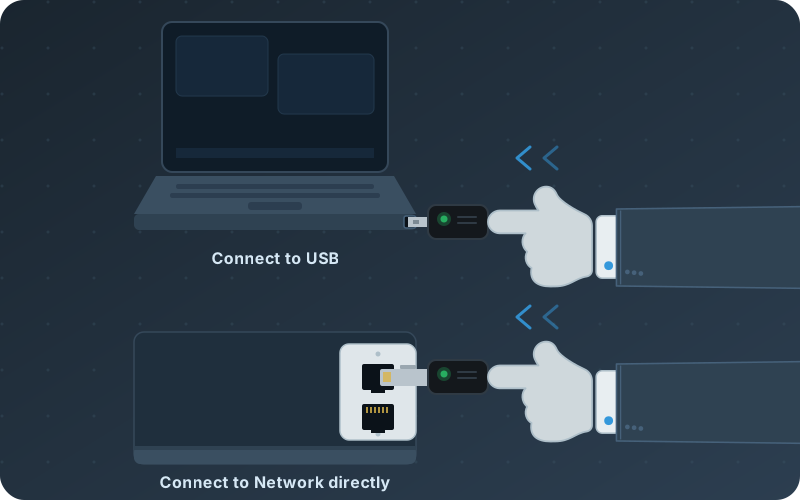
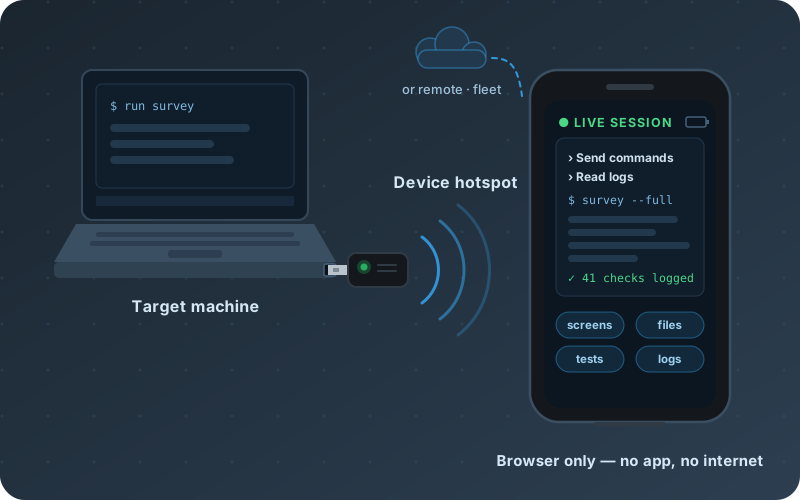
The expert drives the engagement live from a browser: any command with real-time output, in the room over the device's hotspot or remotely through the fleet.
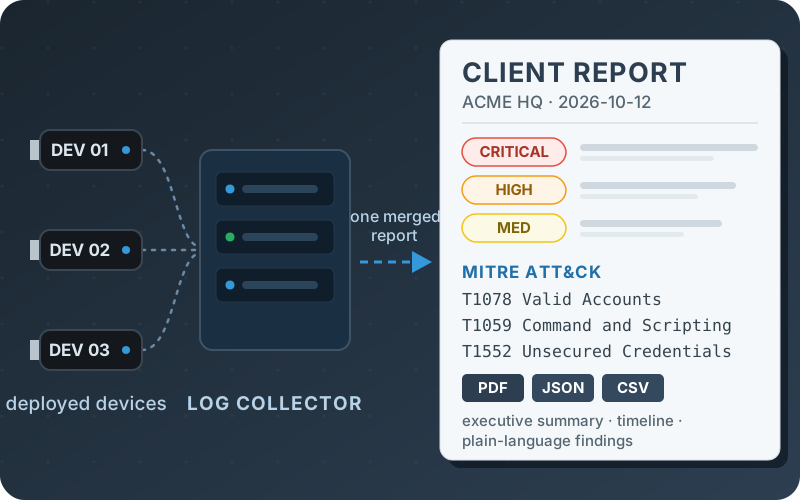
All deployed devices sync their logs to one collector, and the expert generates the severity-rated, ATT&CK-mapped client report remotely. Expert time goes to arming and review only.
A basic Rubber Ducky-class device types one preloaded script and stops there: one payload, one direction, no feedback, no result. The USB Drive Module starts with the same keyboard entry. The difference is everything that happens after.
| Aspect | Basic Keystroke Injection (Rubber Ducky class) | USB Drive Module |
|---|---|---|
| Entry | Types one preloaded script | Detects Windows, macOS or Linux, runs the matching payload and opens a command channel |
| Feedback | None. The operator is blind | Live two-way control: any command, output, files, screenshots |
| Network testing | Not available | Credential traps, impostor responders and traffic interception via the paired Network Module |
| Control after plug-in | None | Phone browser over the device's own hotspot, or remotely through the fleet |
| Multiple devices | Each unit is standalone | Pairing, command relay, log sync: one merged site report |
| Monitoring | Not available | Passive presence: who and what is nearby, encrypted and pseudonymized |
| Result | Nothing is recorded | Severity-rated, MITRE ATT&CK-mapped report, as PDF, JSON or CSV |
| Languages | Payload dependent | 19 keyboard layouts built in |
Choose the right tool for your security assessment needs
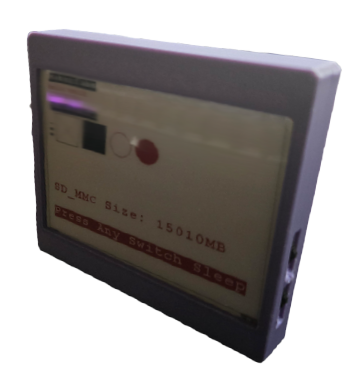
The central hub for coordinating all devices provides real-time monitoring, centralized log collection, and simplified attack orchestration across your entire testing infrastructure.
| Communication Range | Up to 100m (standard Wi-Fi) |
| Device Capacity | Up to 50 simultaneous devices |
| Power Requirements | USB-C powered or battery pack |
| Storage | 32GB onboard storage for logs |
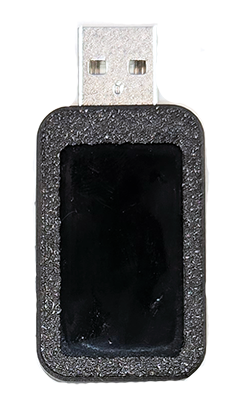
A pocket-sized device for authorized security assessments. Plug it into a computer and it appears as a standard keyboard, detects Windows, macOS or Linux on its own, runs the matching payload, and opens a discreet command channel that gives the operator control of the machine. The typing is only the first step. What happens after sets this module apart.
Control happens from a phone or laptop browser over the device's own Wi-Fi hotspot. No app, no internet connection required. Every engagement ends with a severity-rated, MITRE ATT&CK-mapped report, ready as PDF, JSON or CSV.
| OS Compatibility | Windows / macOS / Linux (auto-detected) |
| Keyboard Layouts | 19 built-in layouts |
| Connectivity | USB (bus-powered) / self-hosted Wi-Fi hotspot |
| Control Interface | Phone or laptop browser. No app or internet |
| Reporting | PDF / JSON / CSV, severity-rated, MITRE ATT&CK-mapped |
| Power Source | USB bus powered |
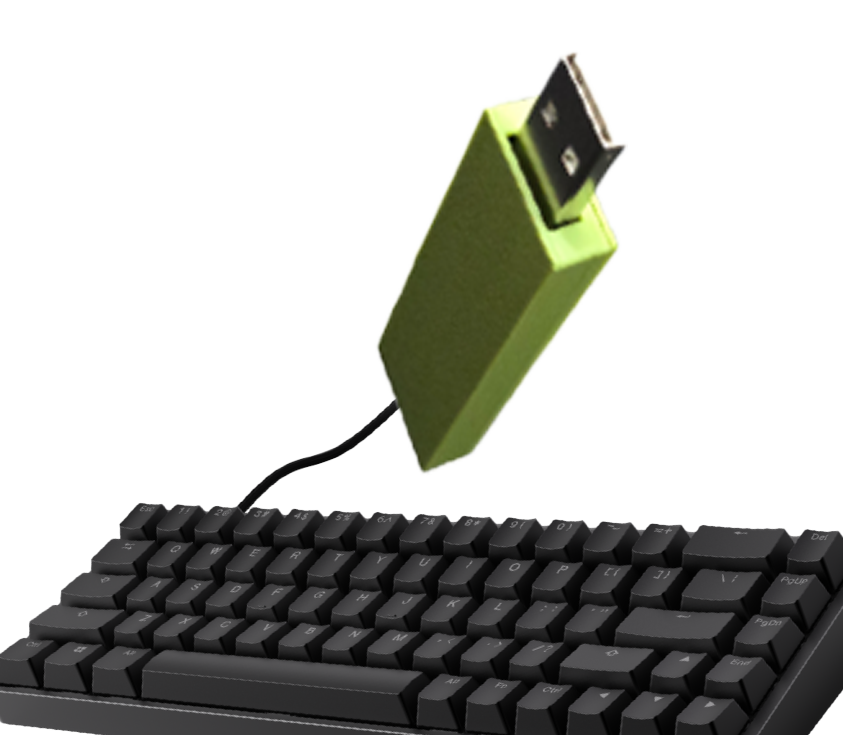
An advanced keyboard logger that sits between the keyboard and computer, capturing all keystrokes while maintaining normal keyboard functionality. Combines all USB Module features with keystroke recording.
| Interface | USB keyboard pass-through |
| Storage Capacity | 2GB keystroke buffer |
| Detection Risk | Very low (hardware-based) |
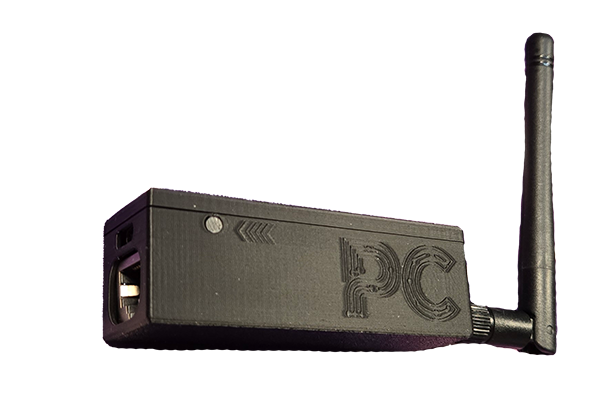
A sophisticated network tap and analysis device that provides deep visibility into network communications. Connects to the LAN network and instantly executes all man-in-the-middle attacks available in the responder tool.
| Network Interface | Gigabit Ethernet (pass-through) |
| Power Options | PoE / USB-C / Battery (4-8 hours) |
| Operating Modes | Passive monitoring / Active MITM |
| Capture Rate | Up to 1 Gbps line rate |
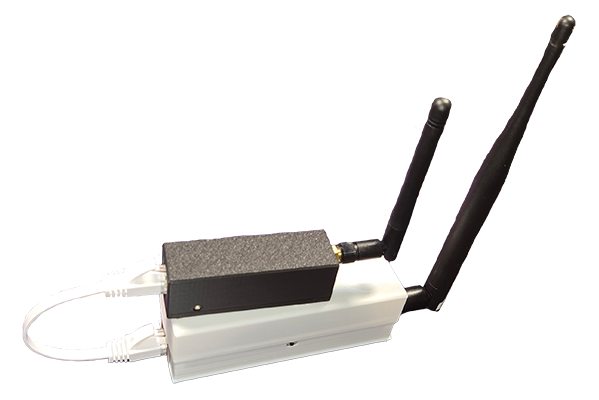
The premium solution for large-scale penetration testing engagements that require an extended command-and-control range. The device acts as an invisible cable, connecting your computer from across the street to the internal network.
| Wi-Fi Protocol | 802.11ah (HaLow) + standard Wi-Fi |
| Range (Line of Sight) | Up to 1000m |
| Range (Urban) | 300-500m |
| Battery Life | 12-24 hours (monitoring mode) |
| Network Features | All Network Module capabilities |
Choose the right combination for your penetration testing needs
| Feature | Command Module | USB Drive | Keyboard Module | Network Module | Long Distance |
|---|---|---|---|---|---|
| Device Management | ✓ | — | — | — | — |
| Endpoint Monitoring | — | ✓ | ✓ | — | — |
| Keystroke Logging | — | — | ✓ | — | — |
| Network Analysis | — | — | — | ✓ | ✓ |
| MITM Attacks | — | — | — | ✓ | ✓ |
| Long-Range Control | — | — | — | — | ✓ |
| Typical Use Case | Central Hub | Endpoint Takeover & C2 | Password Capture | Network Testing | Remote Ops |
Deploy Keyboard Pass-Through and Network Modules in target facility to test physical security controls and data exfiltration paths. Command Module coordinates from nearby location.
Use Network Module with automated MITM capabilities to test network segmentation and credential security. Captures weak authentication protocols and cleartext passwords.
Long Distance Module enables remote command and control from up to 1km away. Ideal for covert testing scenarios where proximity to target must be minimized.
USB Drive Module tests endpoint detection and response (EDR) solutions, USB device policies, and data loss prevention (DLP) controls.
Network Module provides passive reconnaissance to map internal network architecture, identify active services, and discover shadow IT assets.
Test PCI DSS network segmentation, HIPAA encryption requirements, and other compliance controls using Network Module capabilities.
Interested in using our penetration testing devices for your security assessment? Contact us to discuss your requirements, pricing, and rental options.
Contact Sales